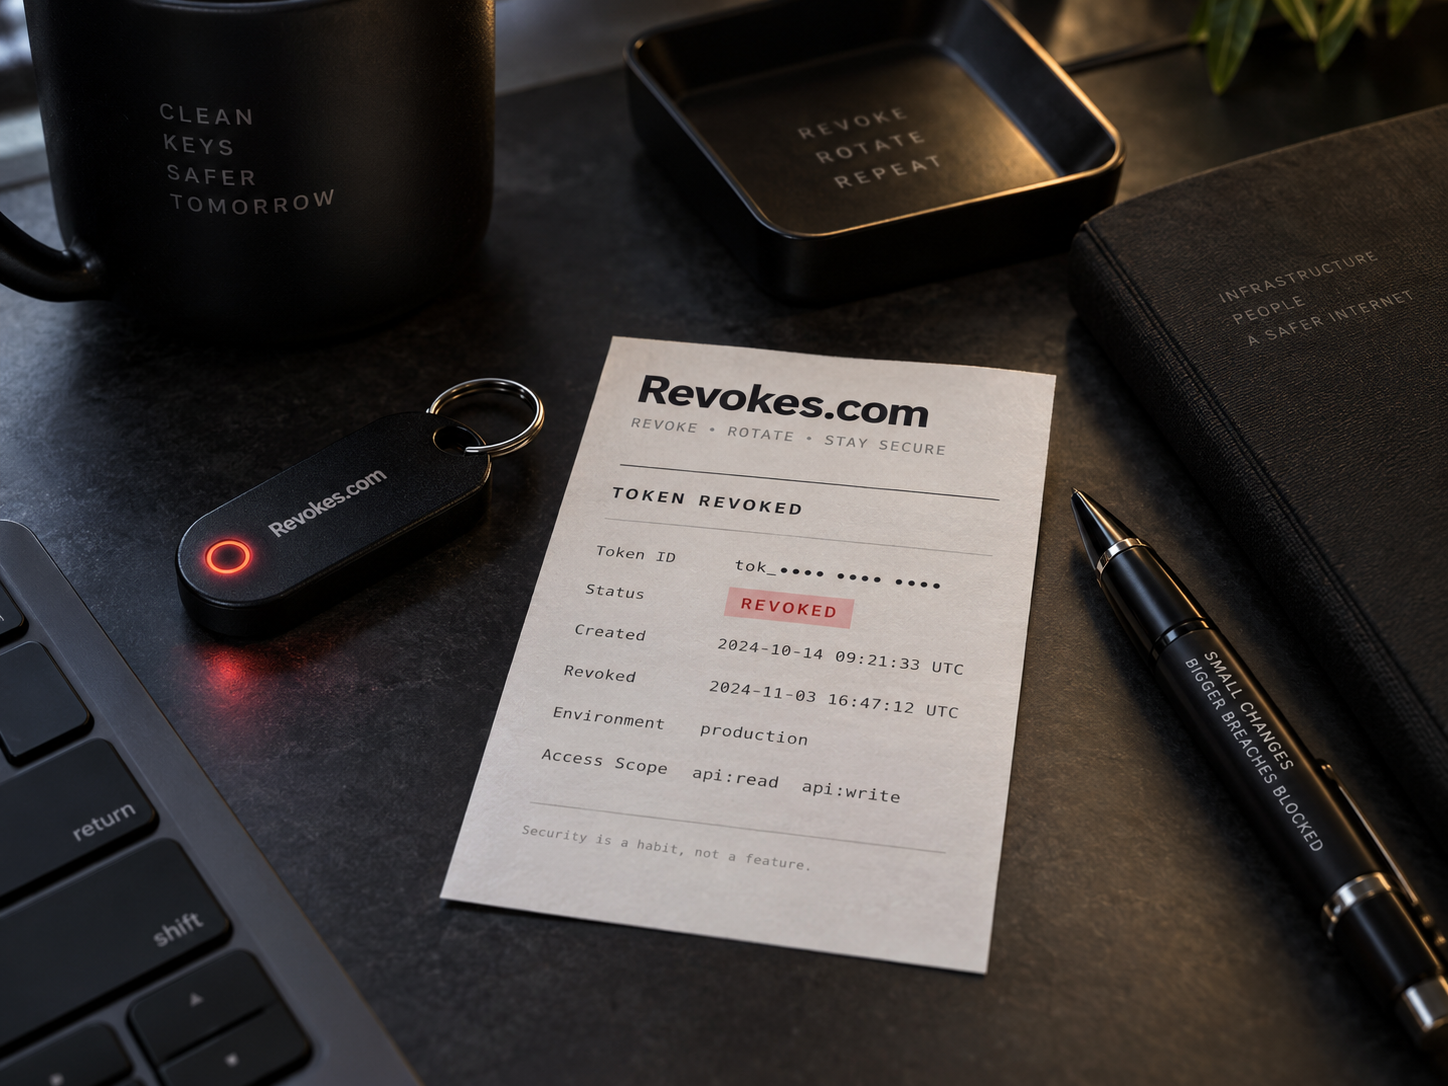
Revokes.com can support several kinds of access products, but each needs a clear first customer and a job worth doing. These four concepts explore different starting points: removing application entitlements, managing credential replacement, ending partner access, and retiring API keys or tokens. They are illustrative business directions. Use them to compare the work involved and to decide which kind of product would make the strongest use of the domain.
Choose the moment the product will own
An access product becomes easier to explain when it begins with a recognizable moment. A person changes roles. A credential needs replacement. A vendor engagement ends. A customer wants to stop an integration. Each moment brings a different set of users, decisions, and systems. Choosing one gives the first offer a boundary. It also helps a founder ask better questions than whether a prospective customer wants a general security platform.
Start by asking an operator to describe the last time they handled that moment. Which record told them what to do? Where did they find the target account or credential? What did they check before calling the task complete? The answers reveal the handoffs and missing information that a product might improve. They also reveal whether the work happens often enough, and causes enough difficulty, to justify a separate tool.
Access removal across applications
The access revoke platform concept centers on an approved change that must reach several applications. Its likely operator is an IT or identity team member. The hard parts include matching identities, identifying the source of a grant, and handling partial completion. A first product could work with a small set of applications and make each result easy to inspect. Connector breadth would matter less than the clarity of the supported operations.
This direction fits a team prepared to maintain integrations and understand their differing behavior. It needs careful scope: removing a group membership is different from disabling an account. It also needs a useful response when one application is unavailable. Read the concept with those questions in mind. A convincing first offer should be able to describe the exact change it performs and what the operator can verify afterward.
Credential ownership and replacement
The credential lifecycle concept begins with the relationship between an issuer, a credential, and the applications that consume it. The customer may be a platform team that needs to replace credentials without losing track of dependents. Its work includes ownership, installation, overlap, and eventual retirement. A record that simply lists secrets would miss much of that job. The product needs to make unfinished replacement visible.
This direction suits a team with a defined credential family and access to the systems that issue it. A first version could focus on one issuer and a small set of consuming applications. The questions to test are practical: can an owner identify the current version, see which consumer is ready, and finish retiring the old version? The article explores the state model and handoffs that would support those decisions.
The end of a partner engagement
Partner offboarding begins with a business relationship rather than a single technical object. An internal sponsor knows that an engagement is ending, while application owners know how to remove individual grants. A useful product could connect those two views. It would need to account for vendors with several engagements, shared accounts, and narrow exceptions for follow-up work. The scope of the relationship matters as much as the list of applications.
This direction may fit a team that understands cross-department coordination. Its first improvement could be a better handoff, even before every action is automated. A sponsor should know what access remains. An application owner should receive a specific task. A coordinator should be able to find the unresolved item and the person responsible for it. The concept looks at how those roles could work from the same engagement record.
A console for API customers
The API key and token concept focuses on a product team’s own customers. A customer administrator needs to identify the right credential, understand its scope, and retire it deliberately. The product can start with one issuer and one permission model. That narrower boundary can make its behavior easier to explain than a console claiming to manage arbitrary credentials from many unrelated providers.
This direction fits developer tools teams that can connect the interface to the actual control surface. Its quality depends on identification, dependency context, and an accurate result. The concept also distinguishes routine replacement from urgent removal, since the two tasks have different intentions. A useful first exercise is to observe someone retire a designated test credential among several similarly named records without help from the product team.
Put the domain against a concrete offer
After choosing a direction, write one sentence naming the buyer and the task. Then list the minimum information needed to perform that task correctly. This exercise gives Revokes.com a practical evaluation: does the name make the subject recognizable to the intended customer, and can the product explain what it does next? The answer will depend on the business being built, not on how many possible features fit beneath the word.
An acquisition inquiry can describe that first offer and the team behind it. There is no need to adopt every concept presented here. A narrower use, or another well defined application of revocation, may be the better fit. Purchase interest and partnership proposals can begin through the inquiry form, with the commercial details and any accompanying assets discussed separately.