The Journal looks at the work that follows a decision to end access. Its articles are written for people who build or operate identity controls, SaaS administration, and credential workflows. The recurring question is concrete: how does a team turn an intended change into a result another person can understand? Start with the guide closest to the task in front of you, then use the related articles to inspect the handoffs around it.
If the control label is unclear
Read “Revoke vs disable” when a product offers several ways to stop access and the consequences are not obvious. The article begins with the object being changed: an account, a grant, a session, or a credential. That distinction matters more than assuming every vendor uses the same verb. A team needs to understand what the selected operation does now and what could happen if a related account is later restored.
A useful way to read the article is alongside one of your own runbooks. Choose a single step and rewrite it as an intended effect in a named system. Then compare that intention with the supported operation. If the runbook says “remove the user” but the task only removes one group, there is a scope question to resolve. The guide provides a way to make that question visible before an operator has to improvise.
The article also treats acknowledgements and observations separately. An application may accept a request before the team can confirm the target state. That difference belongs in the result record. After reading, try to state what evidence your team currently saves for one removal task. If the evidence only proves that a request was sent, decide who owns the later check and how its outcome will be recorded.
If an offboarding request needs coordination
The same-day offboarding checklist is intended for the coordinator who has to work across system owners. It starts with authorization, identity, scope, and timing, then moves through inventory, actions, verification, and exceptions. The list should be adapted to the organization’s own systems and decisions. Its value is in keeping the work visible, especially when some actions are automated and others depend on an application administrator.
Before using it, identify who can decide the scope of the departure or engagement end. A request for a vendor can mean several different things if that vendor works with more than one team. The checklist encourages a clear boundary before broad actions begin. It also separates access removal from content ownership and service continuity, so one unfinished handover does not become an unexplained status for the entire request.
Afterward, use the guide to review the handoff. Could another coordinator identify the open task, its owner, and the next action? Were any exceptions left with a clear purpose and review point? Did an unexpected application appear late in the work? Those questions can lead to small inventory and runbook improvements. A checklist should reflect what the organization learned from using it, rather than remain a generic list of application categories.
If a result needs to be reconstructed later
“Making revoke events audit-friendly” is about readable operational evidence. It separates the decision to remove access, the attempt to perform the operation, and the observation used to confirm the result. This structure helps during support and internal review as well as more formal examination. The article does not claim that a particular schema satisfies every organization’s requirements. It asks whether another person can explain the actual sequence from the records.
Read it with one example event open. Can you identify the target by a stable reference? Does the timestamp describe the request, the execution, or a later check? Is the result a confirmed state or an uncertain outcome after a timeout? These are small wording and data-model questions with practical consequences. An ambiguous “success” field can make a later reader infer more than the system ever observed.
The guide also considers retries, partial completion, and event-writing failures. Those cases deserve attention before a product relies on its history for handoffs. A sample operation that fails once and succeeds later is a useful design exercise. Ask someone outside the implementation team to explain it using only the records. Their questions will often identify missing context faster than another round of polishing field names in isolation.
If access reviews are not leading to changes
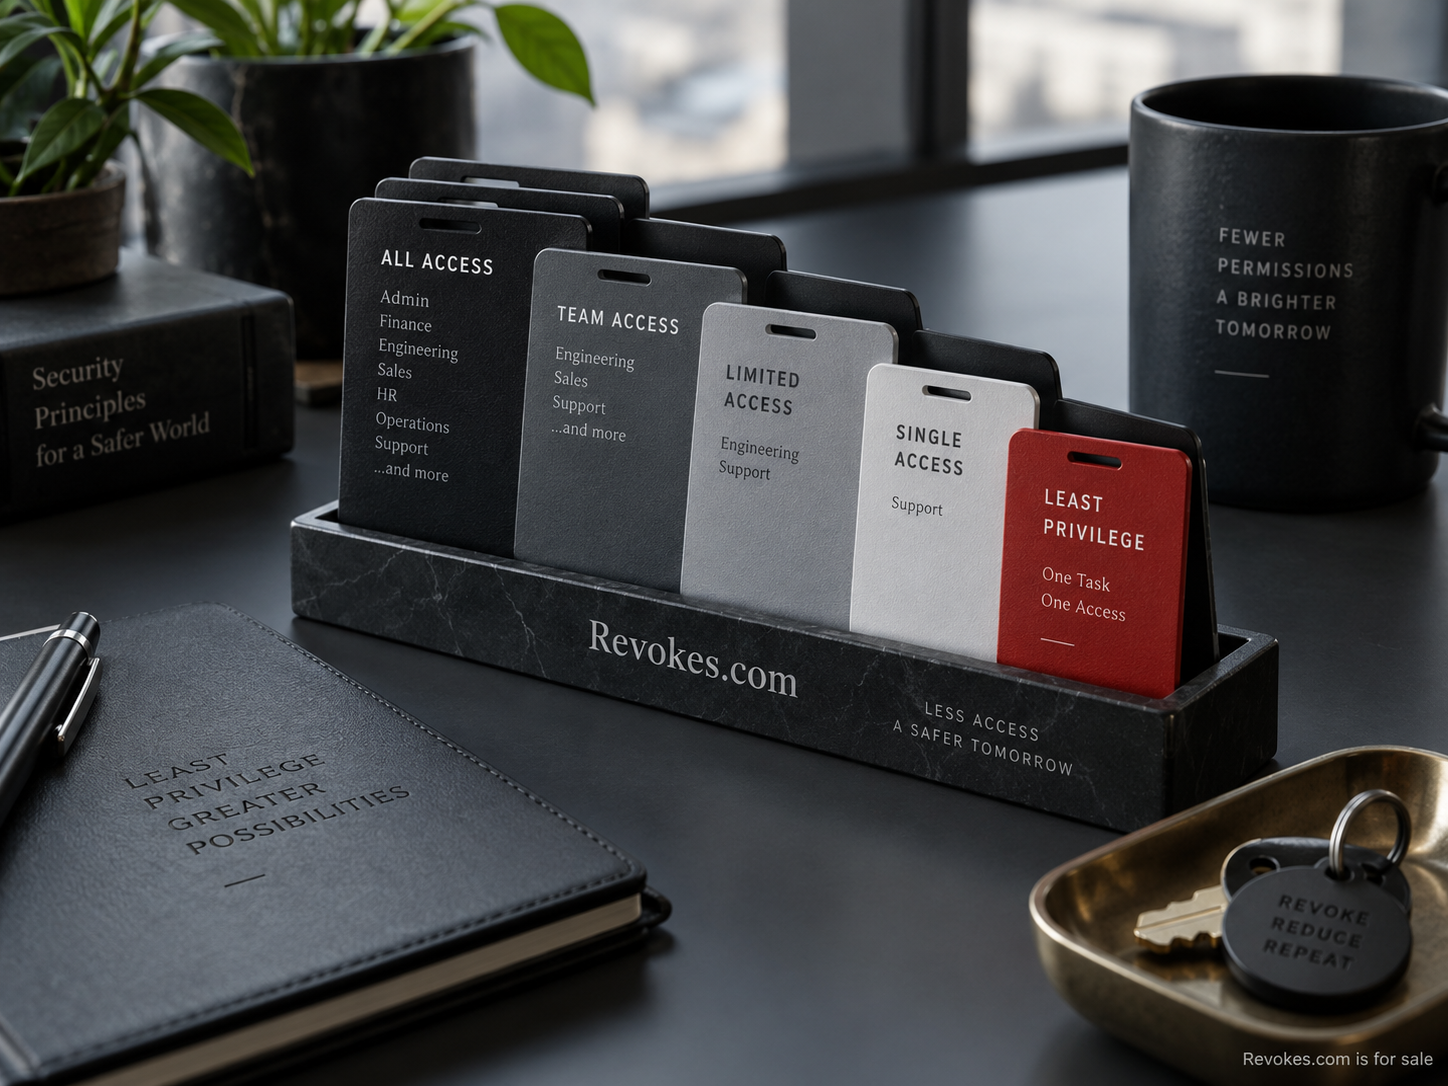
“Least privilege and the revoke path” connects a decision about an entitlement to the route that can remove it. The article looks at purpose, ownership, inherited access, temporary grants, and execution. It is useful when a review produces answers but those answers do not reliably become changes in the target systems. The missing piece may be a specific owner or identifier rather than a more elaborate review form.
Start with a small sample instead of trying to inspect the entire organization at once. Choose a direct grant, an inherited role, and a temporary permission. For each, identify the business reason and the person who can decide whether it still applies. Then trace the removal method and confirmation. This exercise exposes differences that a flat list of users and roles can hide, especially when several relationships supply similar effective access.
The article treats service identities as part of the same ownership problem. A workload may continue for years, yet its purpose and dependencies can change. A review needs a current team owner and application context. A credential’s age or a quiet activity signal cannot explain the whole decision. The goal is a removal path that people can operate with a stated reason and an accurate understanding of the scope.
Read across the handoff
These topics meet at ordinary handoffs. A reviewer decides that access should end. A coordinator assigns the work. An operator chooses the appropriate control. A record explains the result. Weakness in one handoff can make the next step harder even when each team has a reasonable local procedure. The articles use different entry points so readers can inspect the part they own and see what information the next person will need.
Try a short reading session around one completed, non-sensitive example. Have each participant explain their part of the request and the evidence they received. Compare the language used by the reviewer, application owner, and support team. If they use the same word for different states, write down the distinction. A shared definition tied to an actual system is more useful than a broad vocabulary rule that cannot describe the local behavior.
Bring the findings back to the work
A useful outcome from reading is one concrete improvement: a clearer target identifier, a named owner for verification, a better exception record, or a corrected status label. Keep the change small enough to try and specific enough to assess. The next real request will show whether it helps another person act or understand the result. These articles are intended to support that kind of careful operational improvement, with each team responsible for its own implementation and policies.